SAML SSO and Company Login on Aristotto Enterprise
 by Aristotto3 min
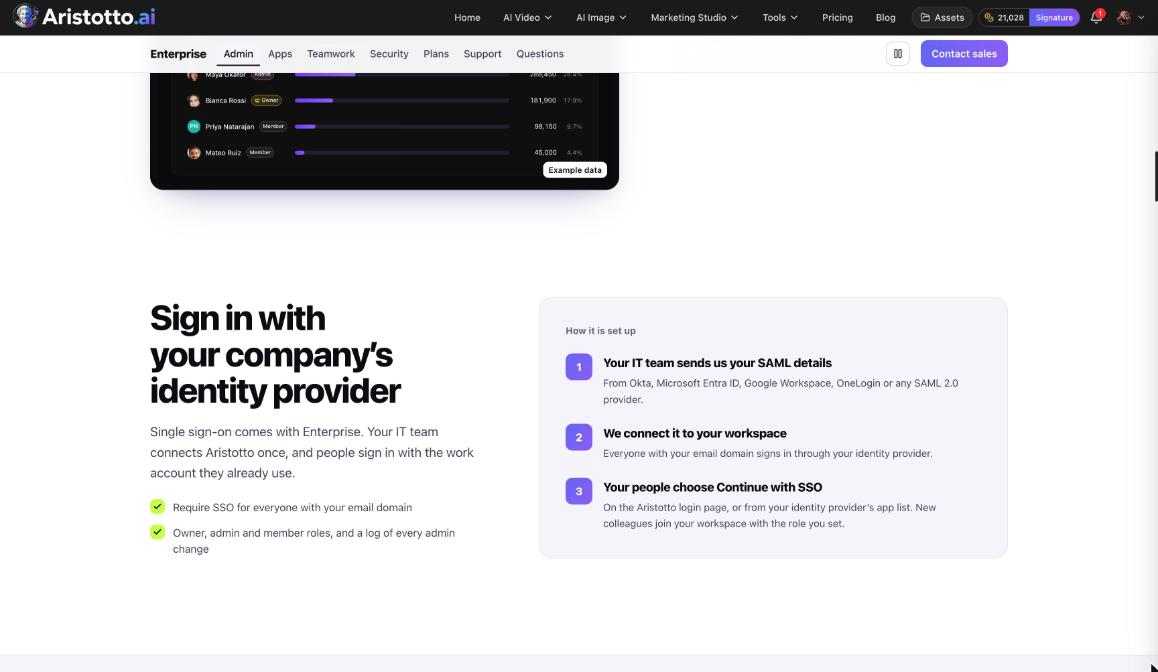
SAML SSO lets everyone with your company's email domain sign in to Aristotto through your identity provider. It is part of Aristotto Enterprise, and SSO can be required for everyone on your domain. Your IT team sends the SAML details, our team connects them to your workspace, and new colleagues join with the role you set.
Identity providers you can use
Okta
Microsoft Entra ID
Google Workspace
OneLogin
Any SAML 2.0 provider
How setup works
Your IT team sends your SAML details to us.
We connect them to your workspace.
Your domain is checked with a DNS TXT record at
_aristotto-verification.<your domain>.You choose whether SSO is required for everyone with your email domain.
You set the role new colleagues join with: member or admin.
SSO is part of going live on Enterprise. When you sign, we connect SSO, load credits and invite admins.
The daily domain check
A daily check looks for the DNS record and emails owners and admins.
| Record status | What happens |
|---|---|
| Missing twice in a row | New company logins pause |
| Missing for 30 days | Company login stops |
Keep the record in place for as long as your team signs in with company login.
How company login works for your people
The first company sign-in opens the existing account with the same email. Nobody gets a second account.
That first sign-in also adds the person to the team with the default role.
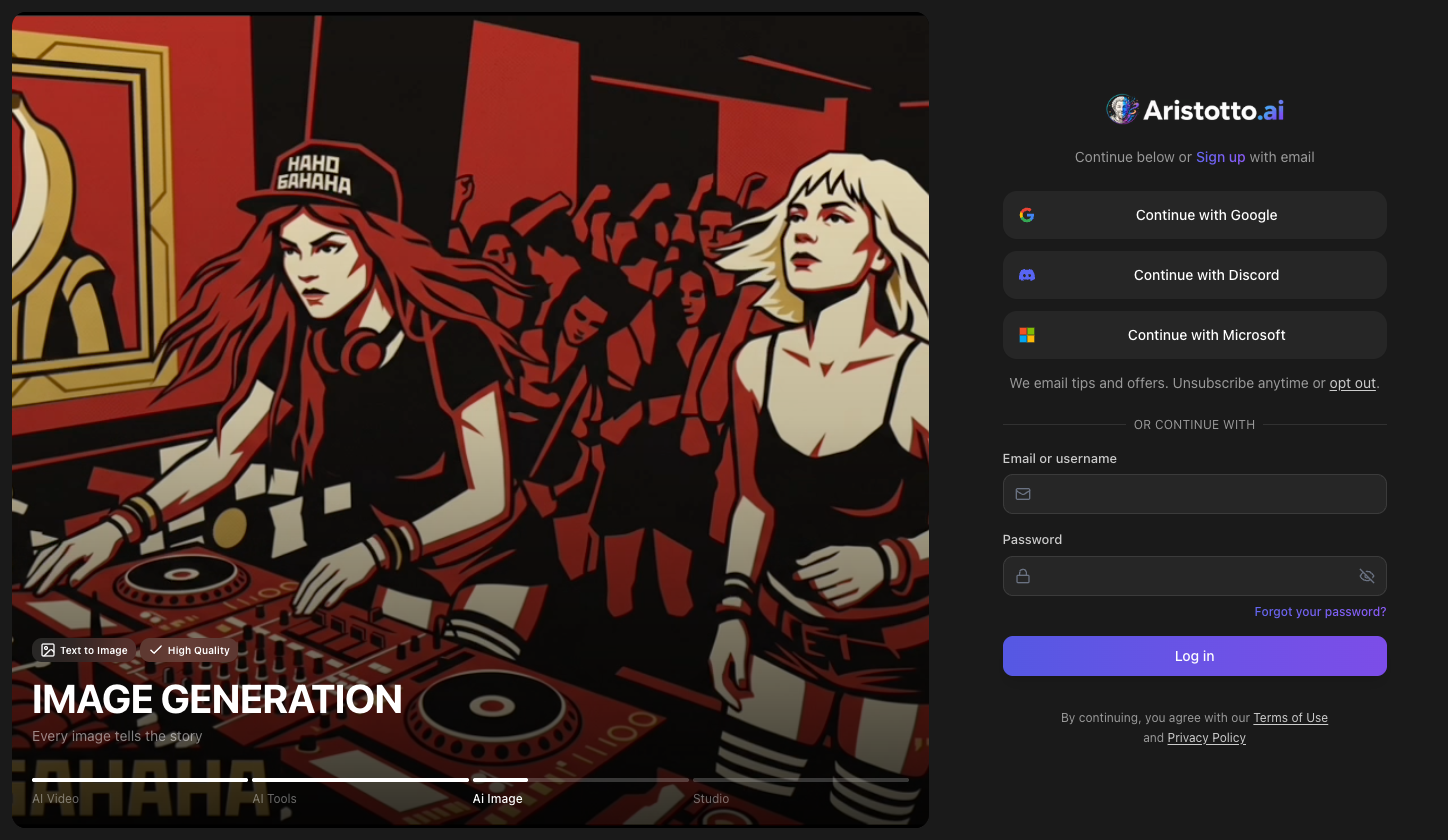
When your company requires SSO, a password or social sign-in is refused and Use your company login appears. The person enters their work email to continue.
People can also start from your identity provider's app list.
A colleague who already has an Aristotto account with their work email keeps that account and joins your team with it.
Roles and the admin record
Enterprise teams use owner, admin and member roles, with a log of every admin change. The team's Activity log records:
joins, including joins through SSO
agreement and SSO changes
invites, role changes, removals and leaves
Owners and admins can search the log and see Change, By, Credits and When for each entry.
If SSO is removed
Sessions opened through the company login end.
Accounts the company login created become regular accounts that sign in by email.
Questions
Which identity providers work with Aristotto?
Okta, Microsoft Entra ID, Google Workspace, OneLogin and any SAML 2.0 provider.
Will people who already have an Aristotto account get a second one?
No. A first company sign-in opens the existing account with the same email and adds the person to the team.
What happens if someone signs in with a password?
When SSO is required for your domain, a password or social sign-in is refused and Use your company login appears.
What if our DNS record goes missing?
If it is missing twice in a row, new company logins pause. After 30 days missing, company login stops.
What happens if we stop using SSO?
Sessions opened through the company login end, and accounts the company login created become regular accounts that sign in by email.